Website security audit, with ♥
What you can't see, a hacker will find
We look for weak spots in your website the way a hacker would, without breaking anything, and explain each one in plain words.
Why get your website audited?
Protect your customers
One poorly protected form, and their names, emails or orders leak out. They trusted you, so keep that trust.
Keep Google on your side
A hacked website gets flagged fast: Google marks it as dangerous and your visitors leave before they even get in.
Avoid nasty surprises
A defaced homepage, a site offline, a mailbox sending spam: better to find the hole before someone uses it.
What we check during the audit
Safer,
more reliable,
worry-free
What shows from the outside
Certificate, security headers, subdomains, forgotten files: everything a curious visitor can find without touching a thing.
Your forms
Contact, quote, login: we check that nobody can slip code into them or submit them in your customers' place.
Versions and plugins
WordPress, plugins, server: an outdated version is a flaw everyone knows about. We track them down one by one.
Your email
Without the right settings, anyone can send an email in your name. We check SPF, DKIM and DMARC.
Sensitive access points
Visible admin pages, publicly accessible backups, default passwords: the doors people forget to close.
What you get
A clear report, made by our own tool
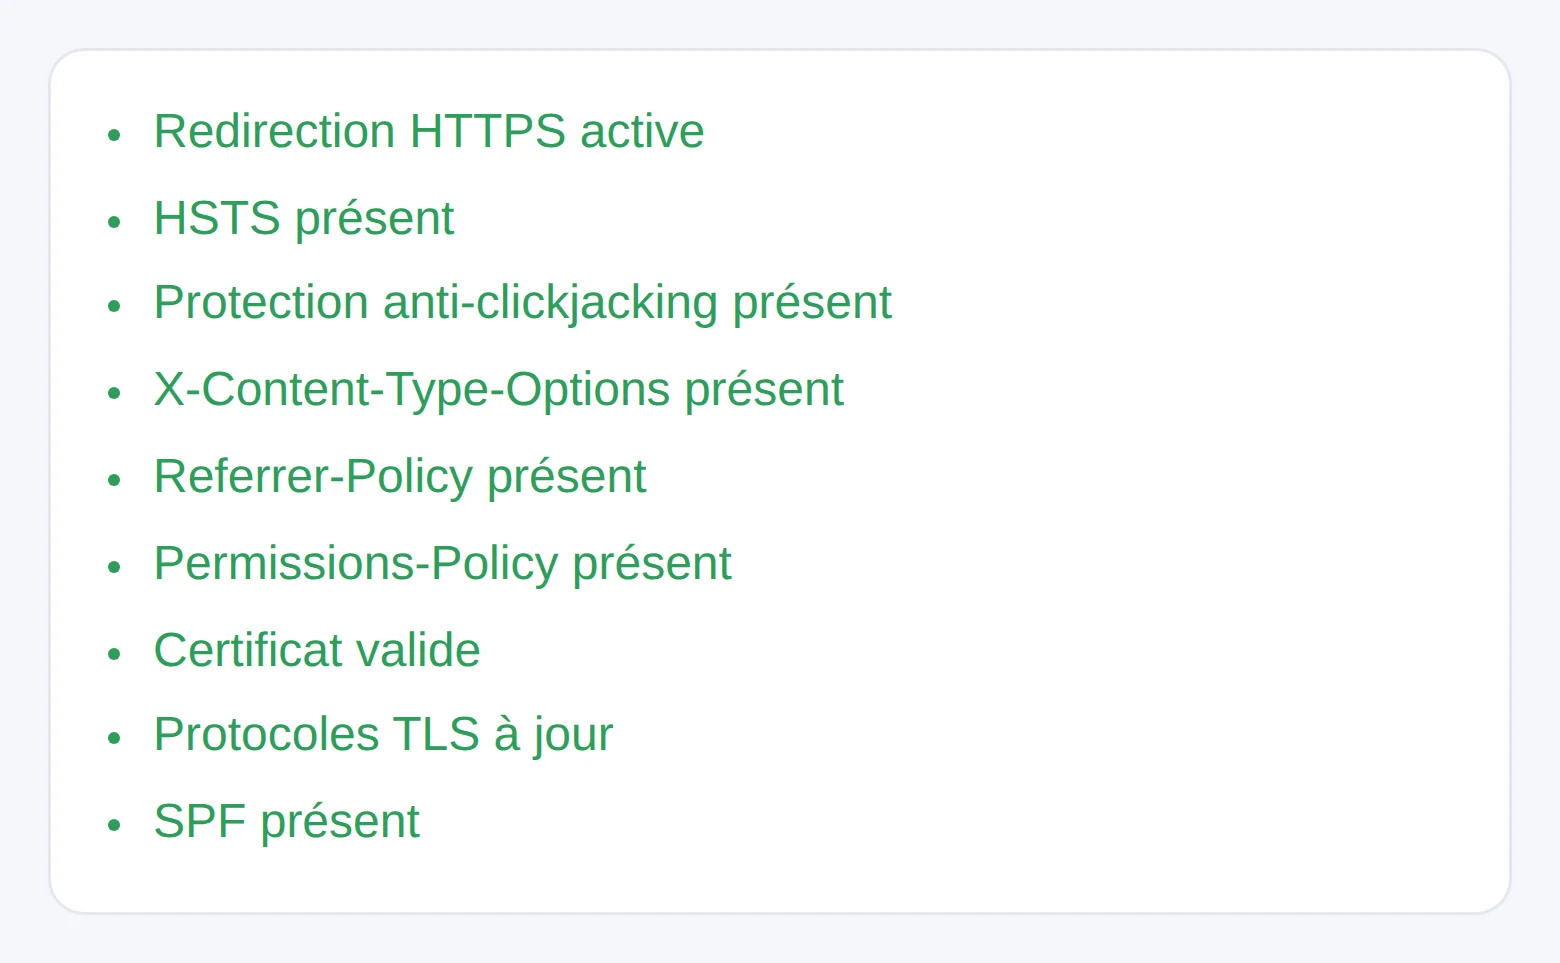
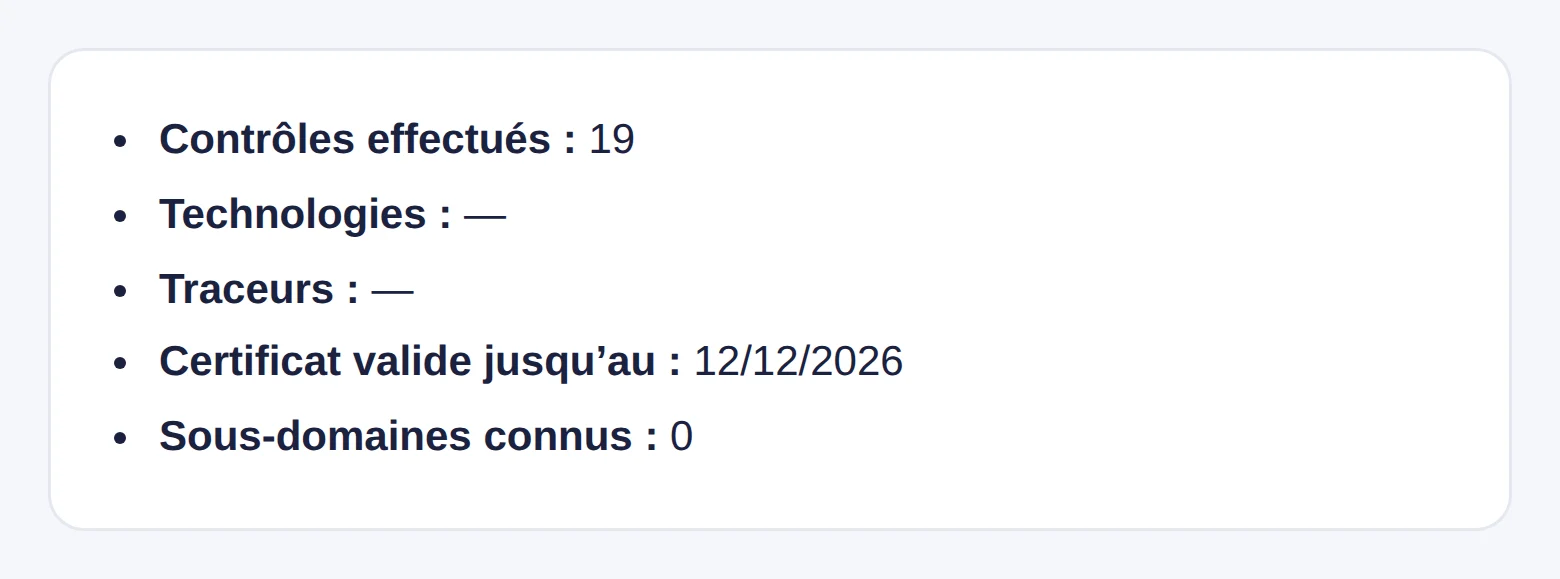
Here's the real report for our own website, llwebsite.fr.
A score and a grade, with the number of issues by severity, so you know right away where you stand.
What it can cause, a concrete example and the fix to make, jargon-free.
The list of protections that work, so you don't worry for nothing.
Certificate, technologies, subdomains: everything we observed about your website.


The steps of an audit
Simple and effective
Your consent first, tests that break nothing, and clear explanations.
A call to scope the audit, then your written consent: the law requires it before testing any website in depth, even your own.
What anyone can see: certificate, security headers, email, files left online, subdomains.
Forms, outdated versions, exposed admin pages: thorough tests that never break anything.
We go over the report with you, issue by issue, from most urgent to least serious, with what needs doing.
We fix things with you or your web provider, then rerun the audit to show you the new score.
- 1
We talk, you sign
A call to scope the audit, then your written consent: the law requires it before testing any website in depth, even your own.
- 2
We look from the outside
What anyone can see: certificate, security headers, email, files left online, subdomains.
- 3
We test in depth
Forms, outdated versions, exposed admin pages: thorough tests that never break anything.
- 4
We walk you through it
We go over the report with you, issue by issue, from most urgent to least serious, with what needs doing.
- 5
We fix and recheck
We fix things with you or your web provider, then rerun the audit to show you the new score.
Got a question?
Yes, with the owner's consent. For in-depth tests, the law requires written authorization: we have you sign it before we start, and we touch nothing without it.
No. Our tests are designed to change or delete nothing: we check whether a door is open, and we never force it.
Yes: WordPress, Shopify, Wix or custom-built, we audit every kind of website. If another provider looks after it, we send them the list of fixes.
It's quoted case by case: we give you the exact price after the first call, based on the size of the website and the depth of testing.
A report with a score out of 100, the list of passed checks and issues found, each one explained simply with its fix.
We rerun the audit to confirm everything is closed up, and we can keep watch over your website afterward as part of maintenance.